Everybody knows that!
Adrian A. BaumannSenior Security Officer, BIT
Warning: This presentation contains exaggeration, sarcasm, reductio ad absurdum and other potentially hazardous rhetorical devices. Exposure may cause established beliefs to be questioned.
Ἄνδρα μοι ἔννεπε, Μοῦσα, πολύμηχανον, ὃς μάλα πολλὰ πλάγχθη, ἐπεὶ Τροίης ἱερὸν πύρινον τεῖχος ἔρρηξεν· πολλῶν δ’ ἀνθρώπων ἴδε τρωτὰ ἔργα καὶ νόον ἔγνω, σπεύδων τὸν περίβολον ἀσφαλίζειν καὶ χρήστας φυλάσσειν. ἀλλ’ οὐδ’ ὣς ἑτάρους ἐδύνατο σῶσαι, ἱέμενός περ· αὐτῶν γὰρ ἀφραδίῃσιν ἀπώλοντο, νήπιοι, οἳ τὰ αὐτὰ συνθήματα αὖτις ἐχρῶντο καὶ τὰ συνημμένα ἤνοιγον.
Tell me, Muse, of the man of many exploits, who wandered far after he had breached Troy’s holy firewall. He saw the vulnerabilities and learned the minds of many men, striving to secure his perimeter and protect his users. Yet he could not save them, for in their folly they reused their passwords and opened the attachments.
Tell me, Muse, of the man of many exploits, who wandered far after he had breached Troy’s holy firewall. He saw the vulnerabilities and learned the minds of many men, striving to secure his perimeter and protect his users. Yet he could not save them, for in their folly they reused their passwords and opened the attachments.
Myth: A story or belief that is not necessarily based on fact.
Security Myths
Tell me, Muse, of the man of many exploits, who wandered far after he had breached Troy’s holy firewall. He saw the vulnerabilities and learned the minds of many men, striving to secure his perimeter and protect his users. Yet he could not save them, for in their folly they reused their passwords and opened the attachments.
Myth: A story or belief that is not necessarily based on fact.
Security Myths
Not completely wrong...
just right enough to be believed
Everybody knows that!
Everybody knows that!
Including us.
Everybody knows that!
Including us.
Especially us.
Especially us.
And that's the problem!
Let's talk...
Let's talk...
- Websites
Let's talk...
- Websites
- Passwords
Let's talk...
- Websites
- Passwords
- Best Practice
Let's talk...
- Websites
- Passwords
- Best Practice
- Common Sense
Websites
Websites
Question to the group: What needs to be considered when surfing?
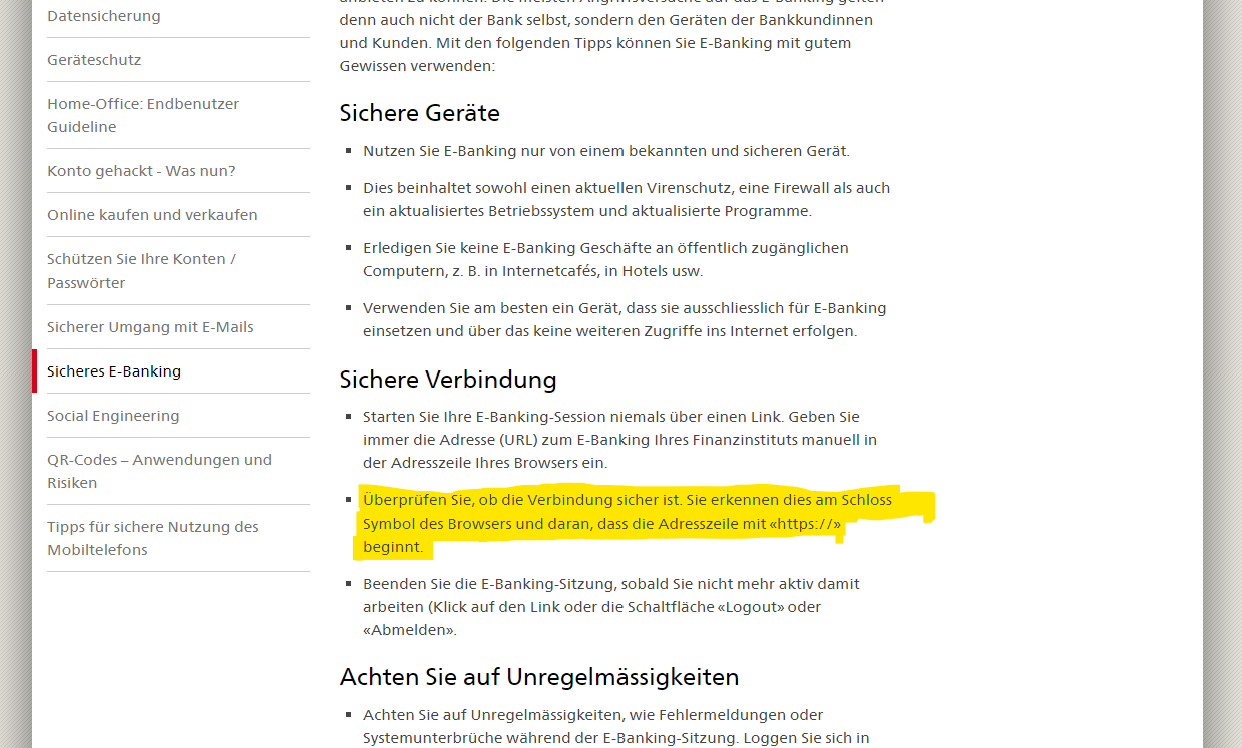
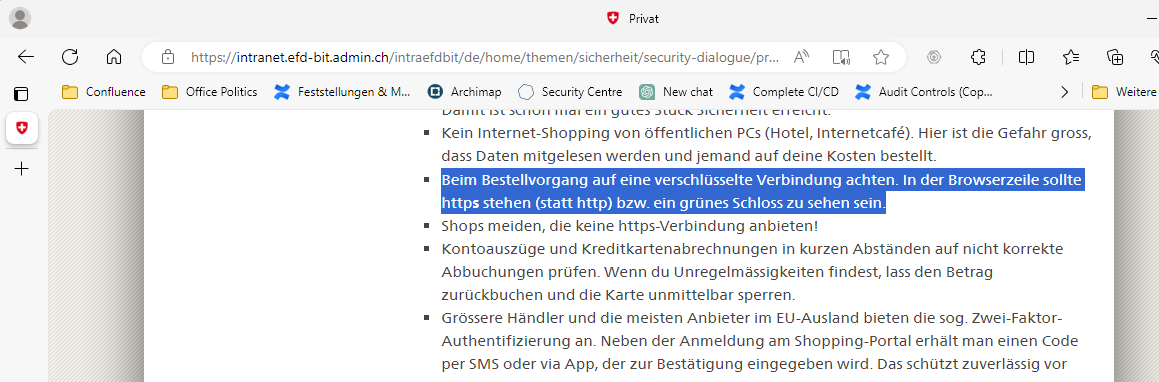
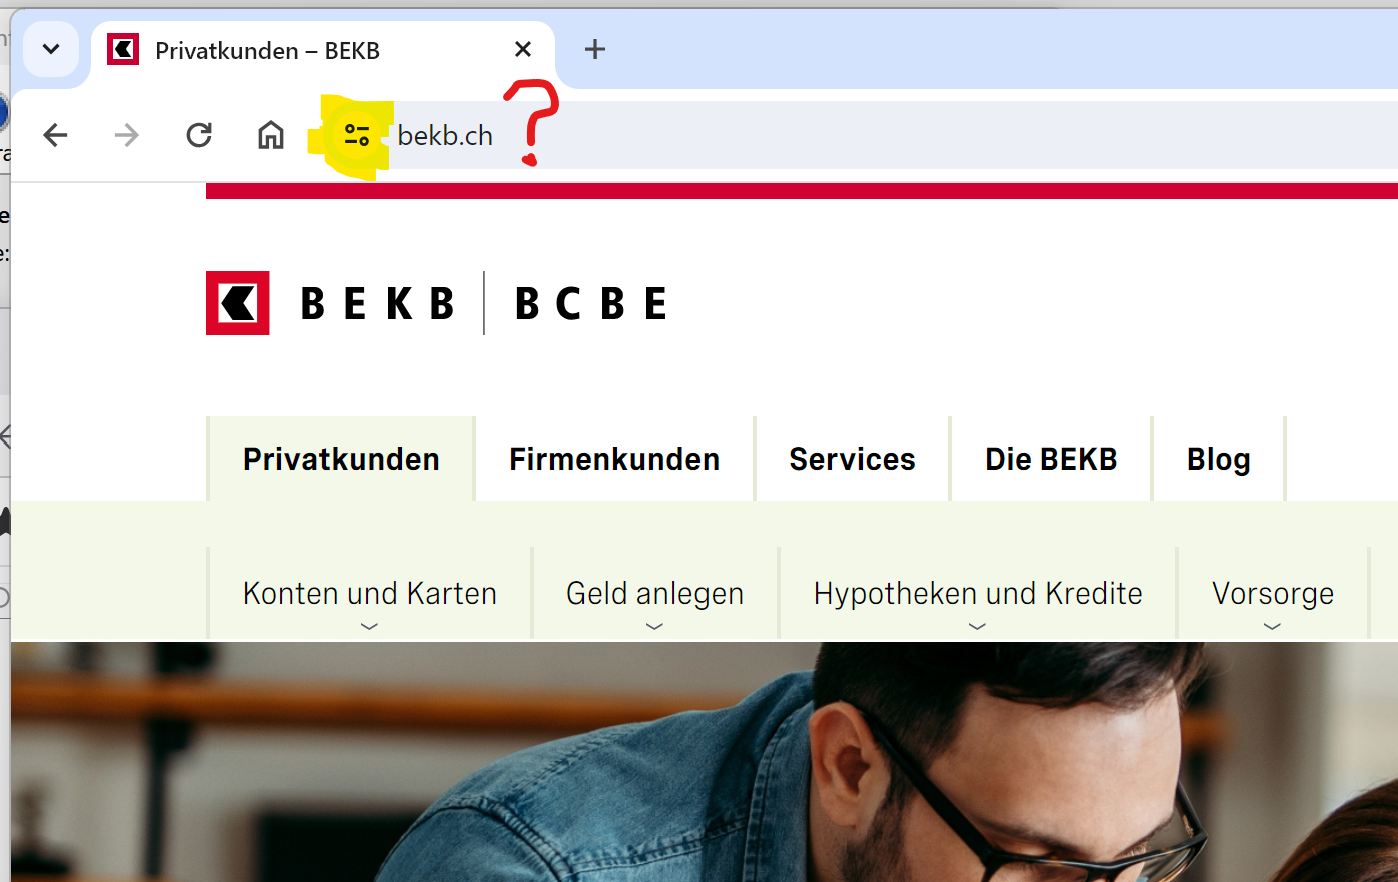
The lock in the browser
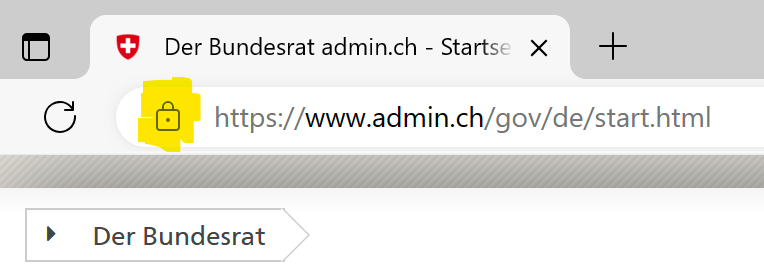
As seen at: BACS
As seen at: BIT
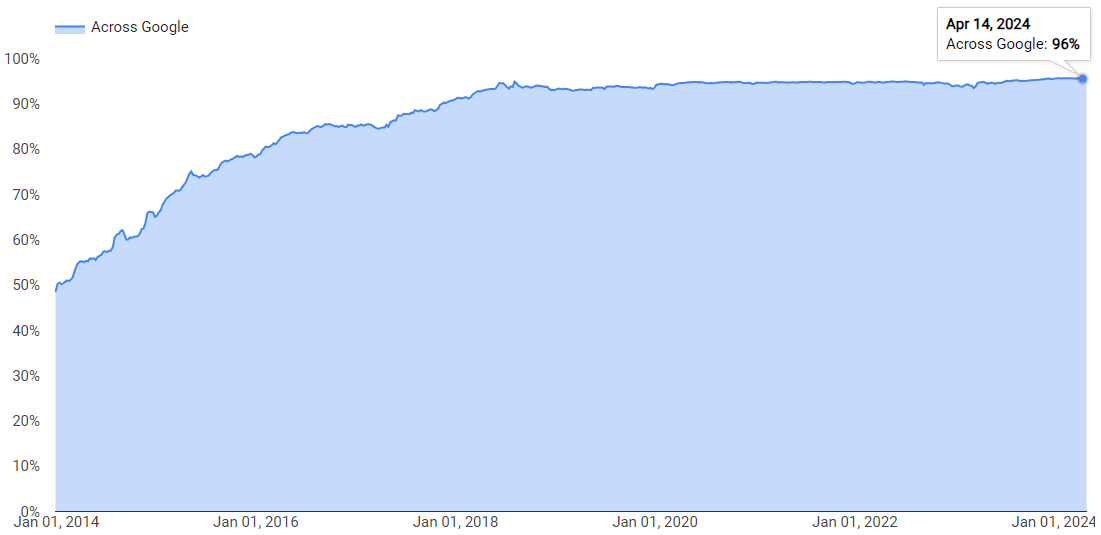
https:// today:
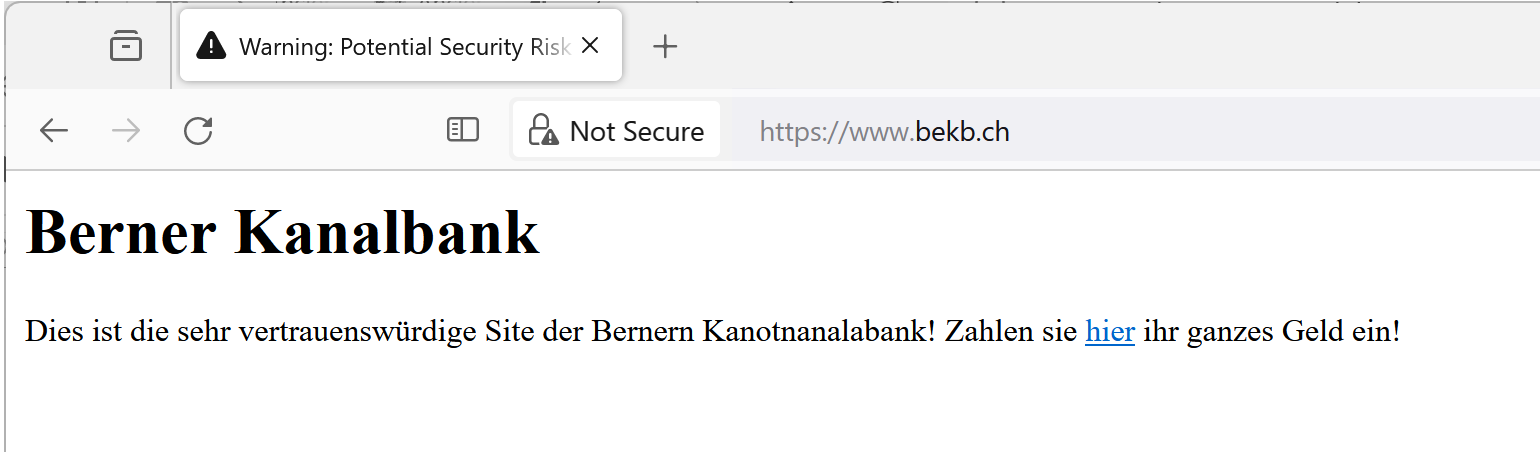
Let's try it out.
The browsers have responded
But still...
https://bbc.co.uk1
can be trusted.
1 or blick.ch
srf.ch
derbund.ch
newyorktimes.com
...and your favourite website
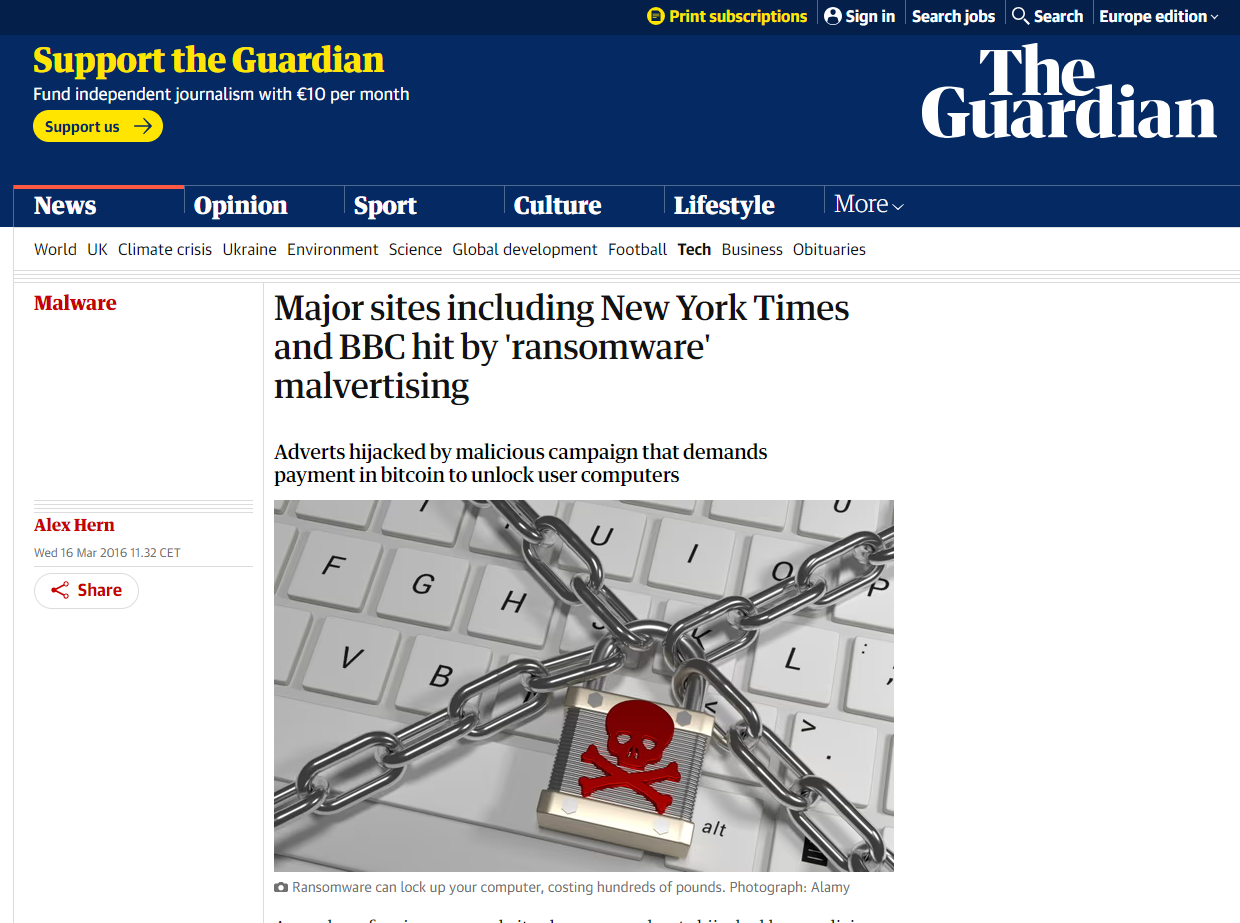
...not as long as they show ads!
...not as long as they show ads!
P4s5wordZ!
A good password...
Yes? What about good passwords?
A good password needs to contain:
- Capitals
- Lower case letters
- Numbers
- Special characters
- Emojis
- An extinct mammal
- Two postage stamps, one of which used
- At least one Chinese logogram
- A non-radioactive isotope of an alkali metal
- A potted plant
- Three non-latin letters from at least two different extinct languages
- 100g of plain flour and 50g of unsalted butter
- The Answer to Life, the Universe, and Everything
Entropy
\[\begin{equation} E=\log_2(N^L) \end{equation} \]
where:
- \( E = \) Entropy, measured in bits
- \( N = \) Number of possible characters
- \( L = \) Password length
Number of possible passwords: \( 2^E \)
Entropy
should be > 75 bit
37'778'931'862'957'161'709'568
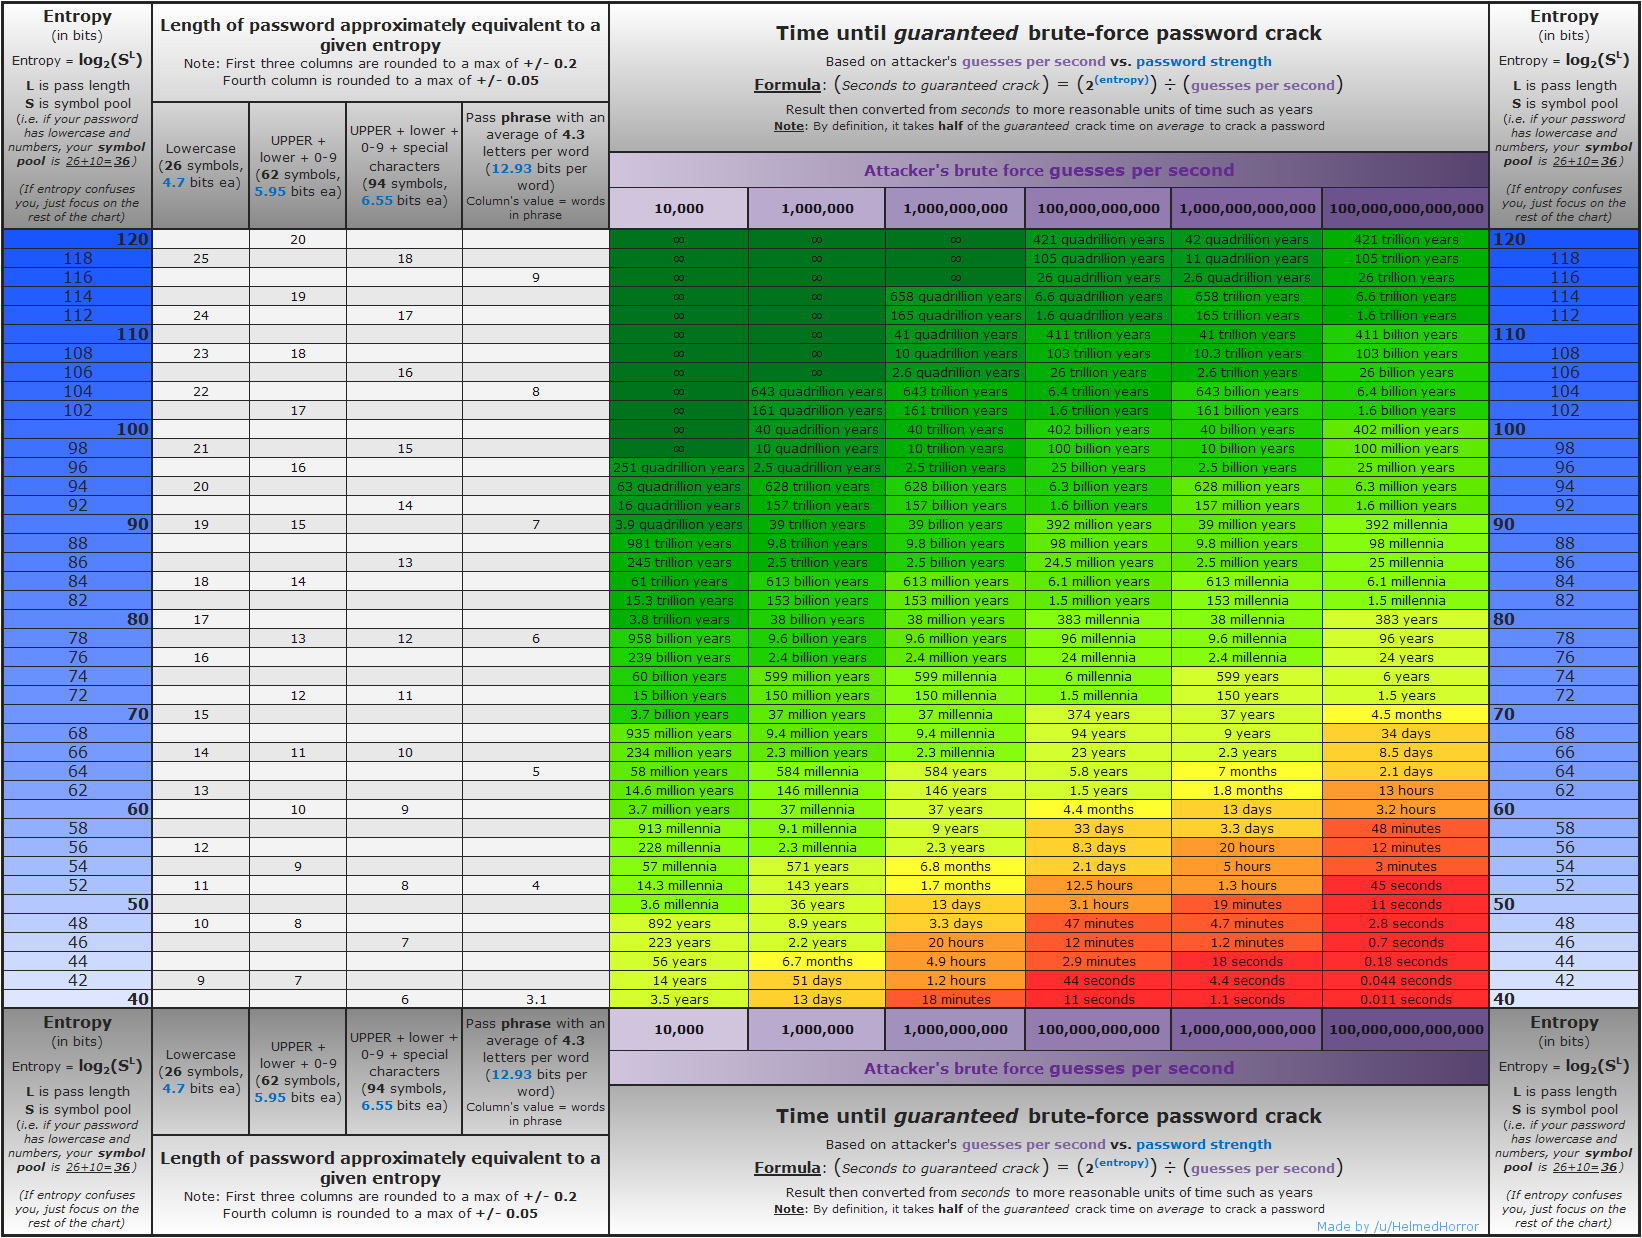
Entropy
| Rule | N | L | E |
|---|---|---|---|
| Upper,Lower,Numbers × 10 | 62 | 10 | 60 |
| Upper,Lower,Numbers × 13 | 62 | 13 | 78 |
| Lowercase only × 17 | 26 | 17 | 80 |
| English words × 6 | 7776 | 6 | 78 |
78 Bit Entropy
j9P0tx8XyqR9sR
78 Bit Entropy
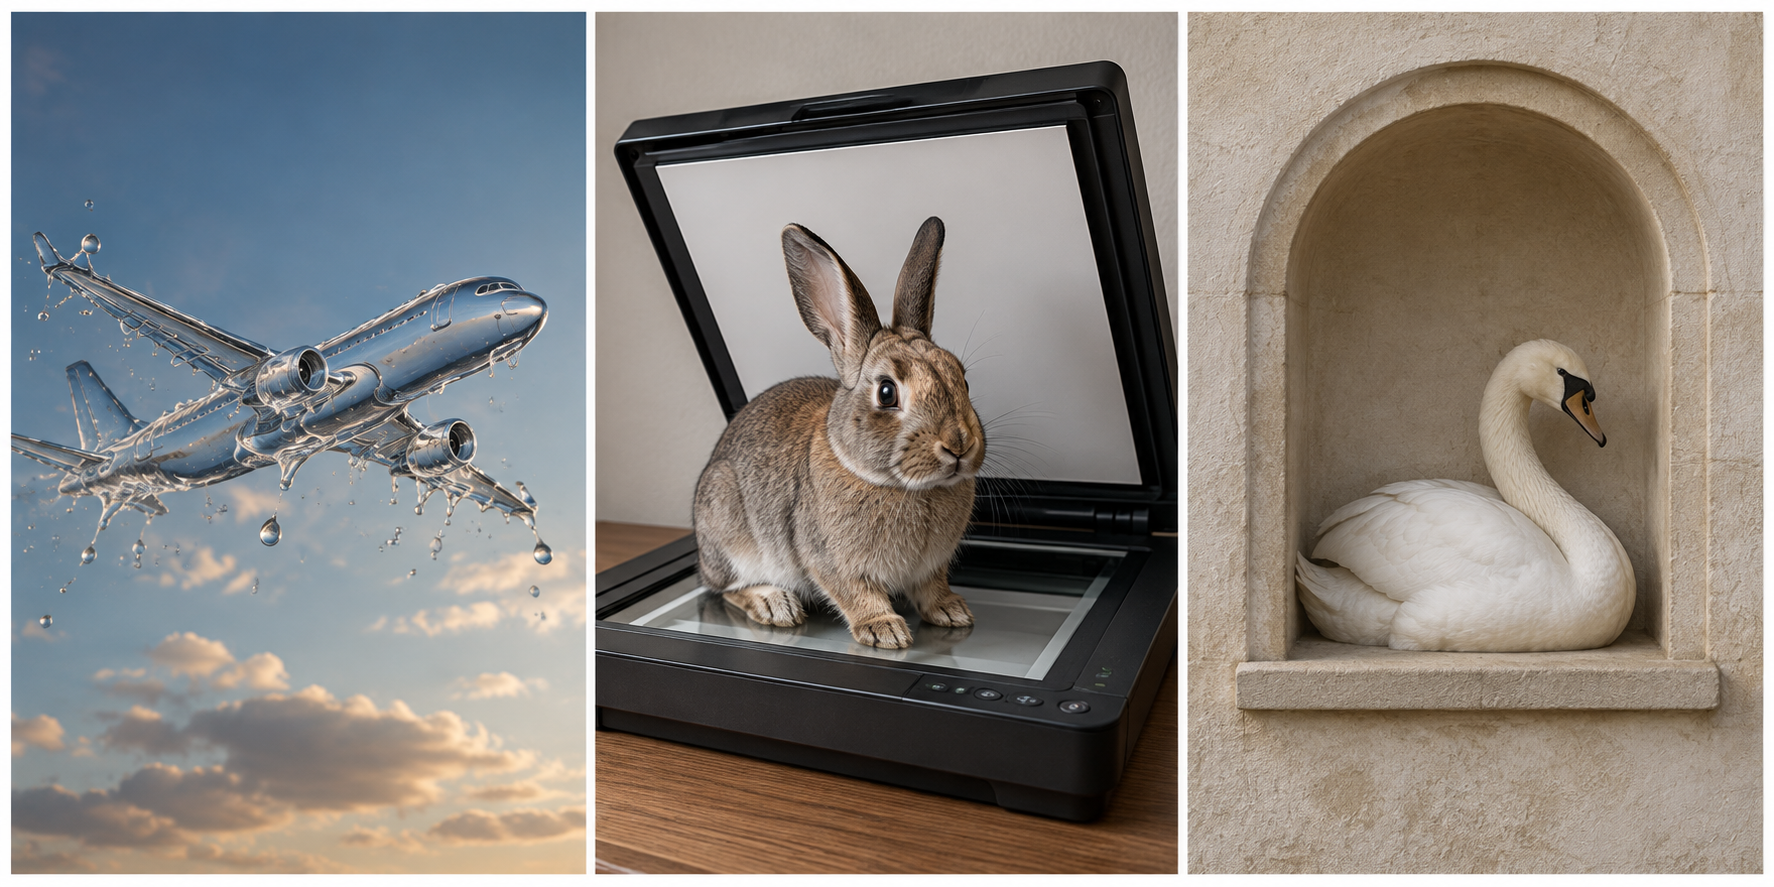
LiquidPlaneBunnyScanNicheSwan
78 Bit Entropy
LiquidPlaneBunnyScanNicheSwan
More Password Myths:
- Change every 3 months
- Don't write them down
- 2FA protects you from phishing
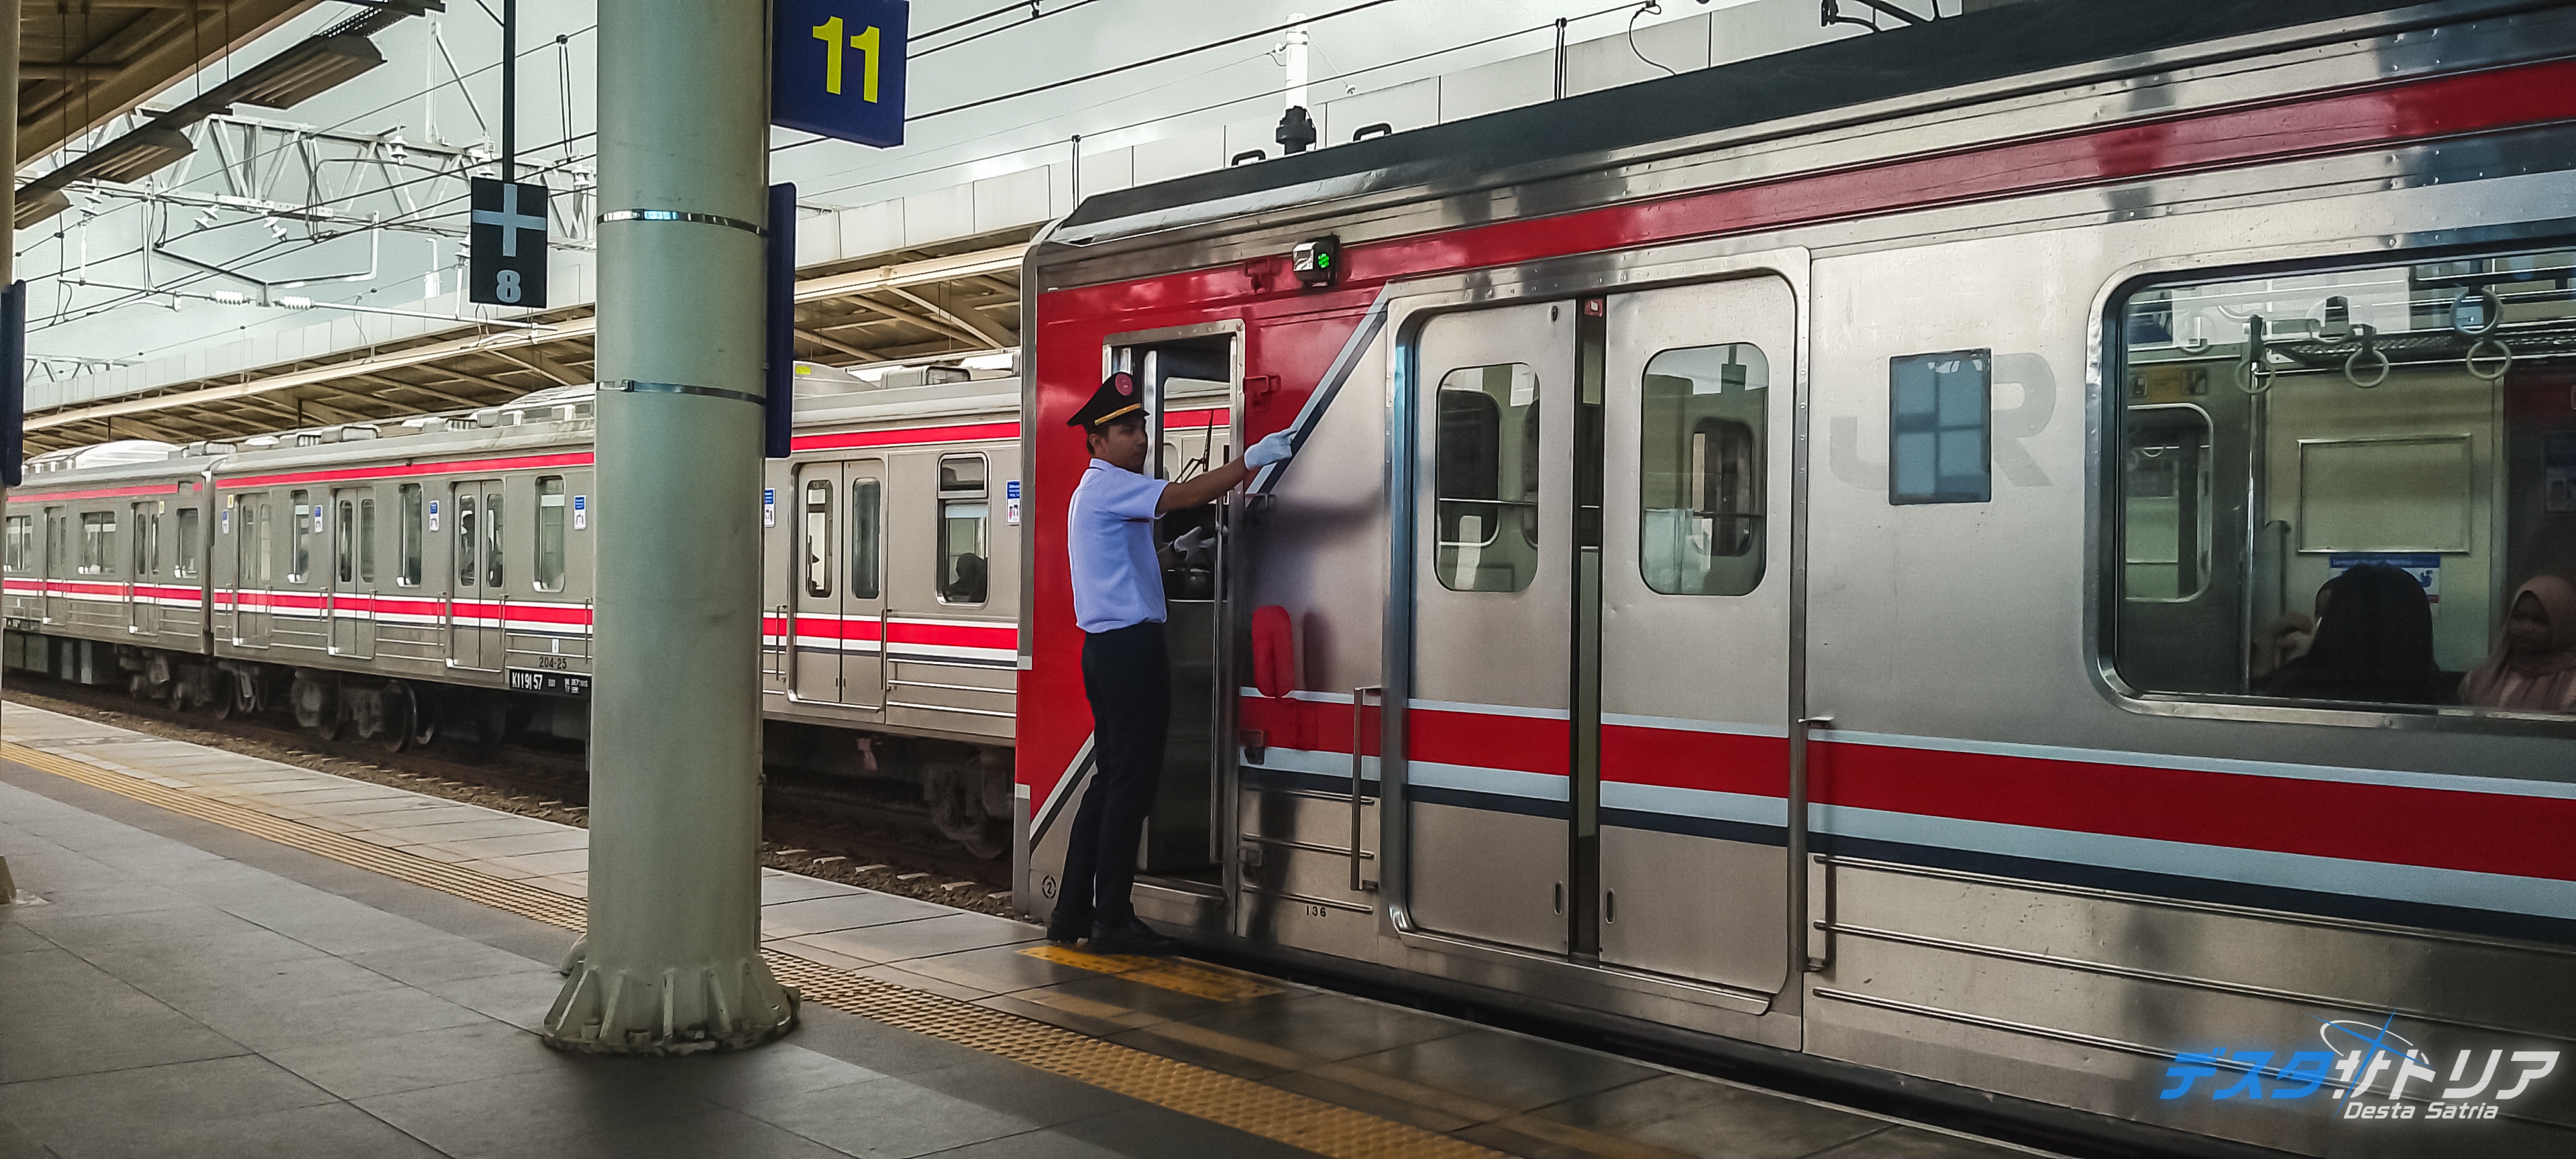
Best Practices
Deleting Data
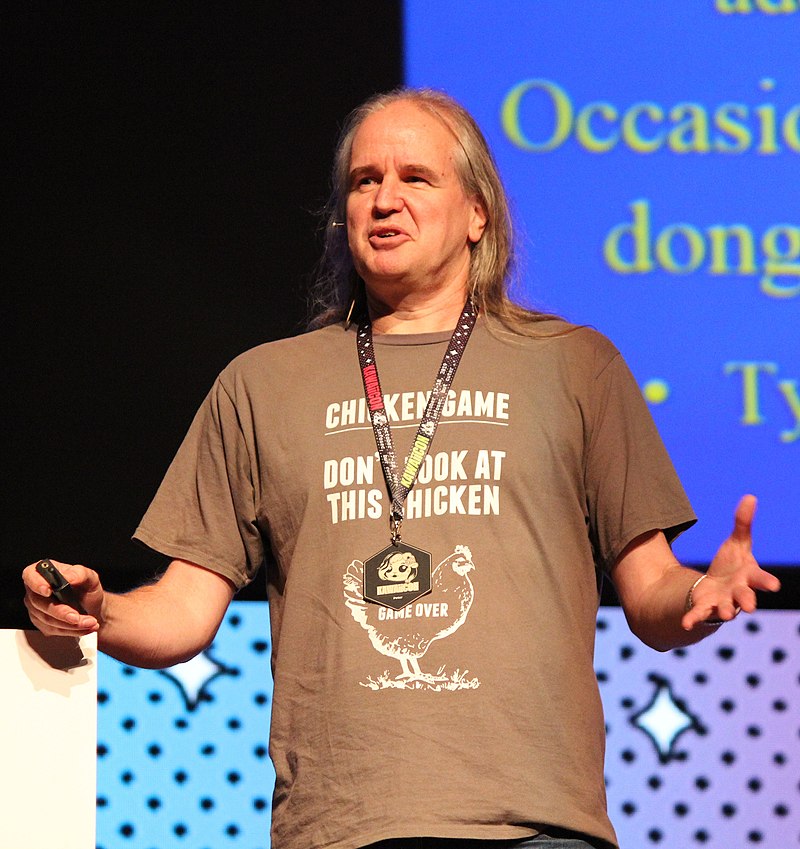
How often do you write over sensitive data?
Deleting Data
Deleting Data
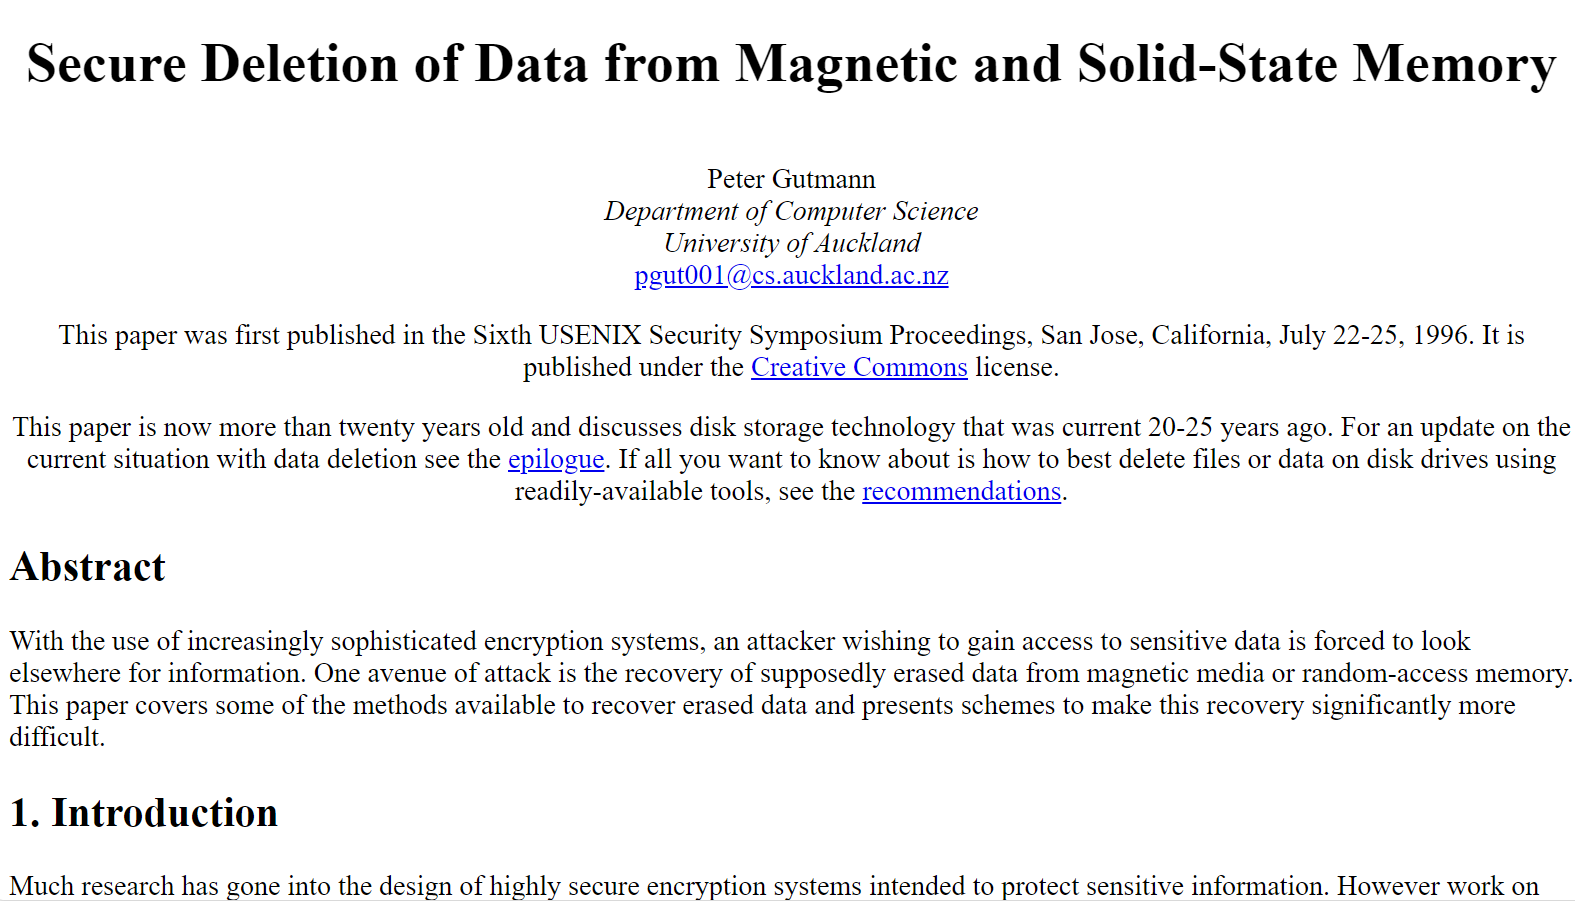
35 times.
Deleting Data
Magnetic Remanence
Inexact Tracking
Deleting Data
Magnetic Remanence
Inexact Tracking
Irrelevant at today's data density...
And SSD have neither magnets nor tracks!
Deleting Data
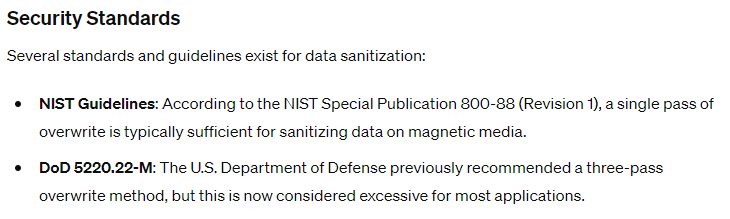
Single file wipe does absolutely nothing on SSDs.
That's why we encrypt "hard disks"...
or...
Deleting Data
Patching
We patch our systems every day, we're secure.
Patching
We patch our systems every day, we're secure.
Good!
Patching is necessary, important and insufficient.
Patching
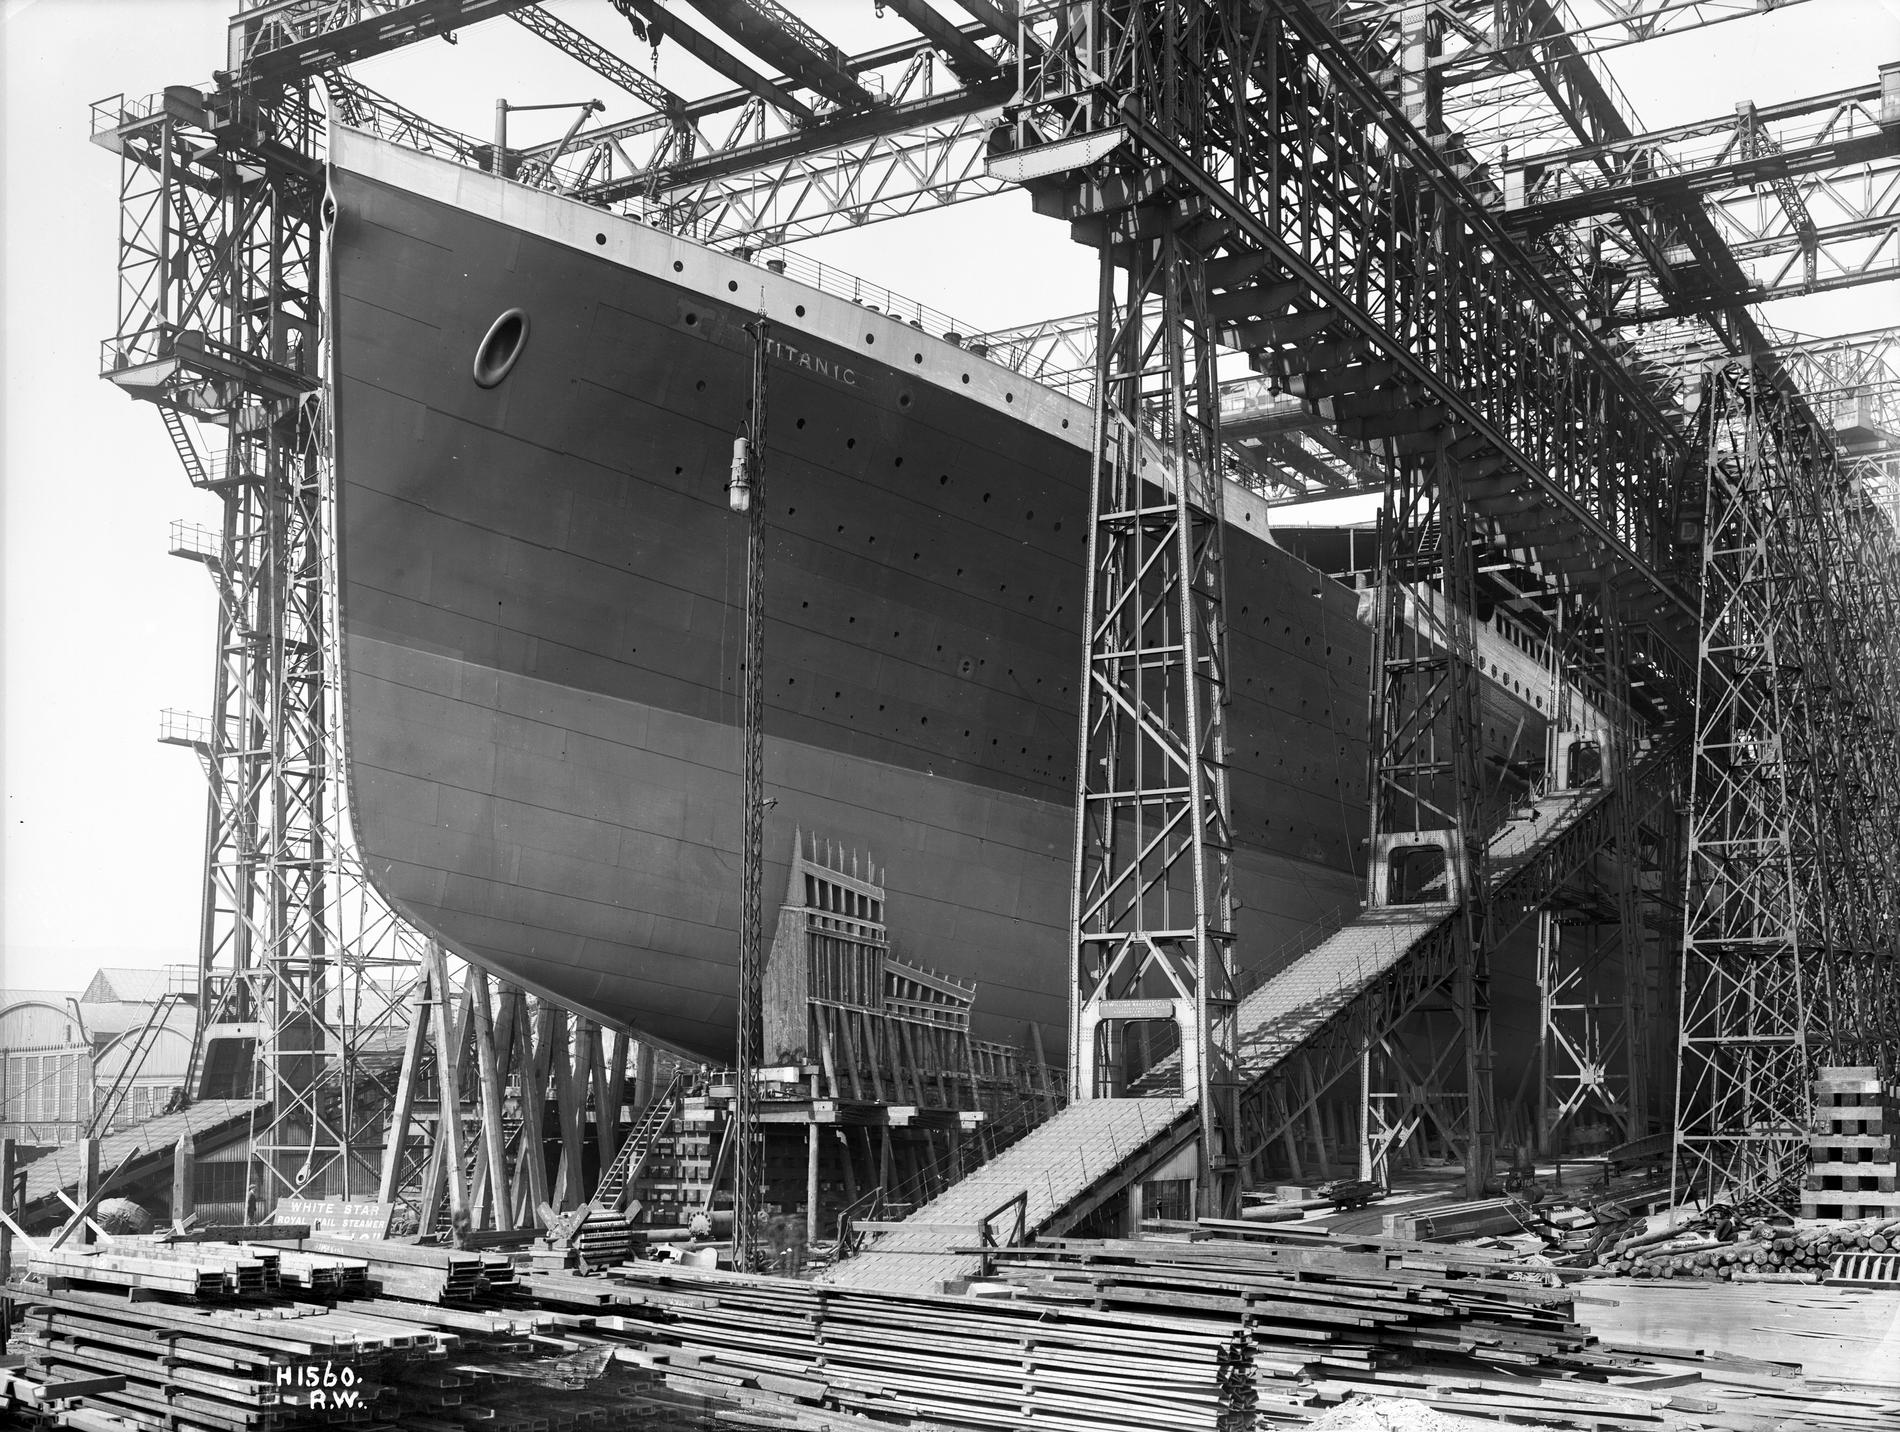
Patching
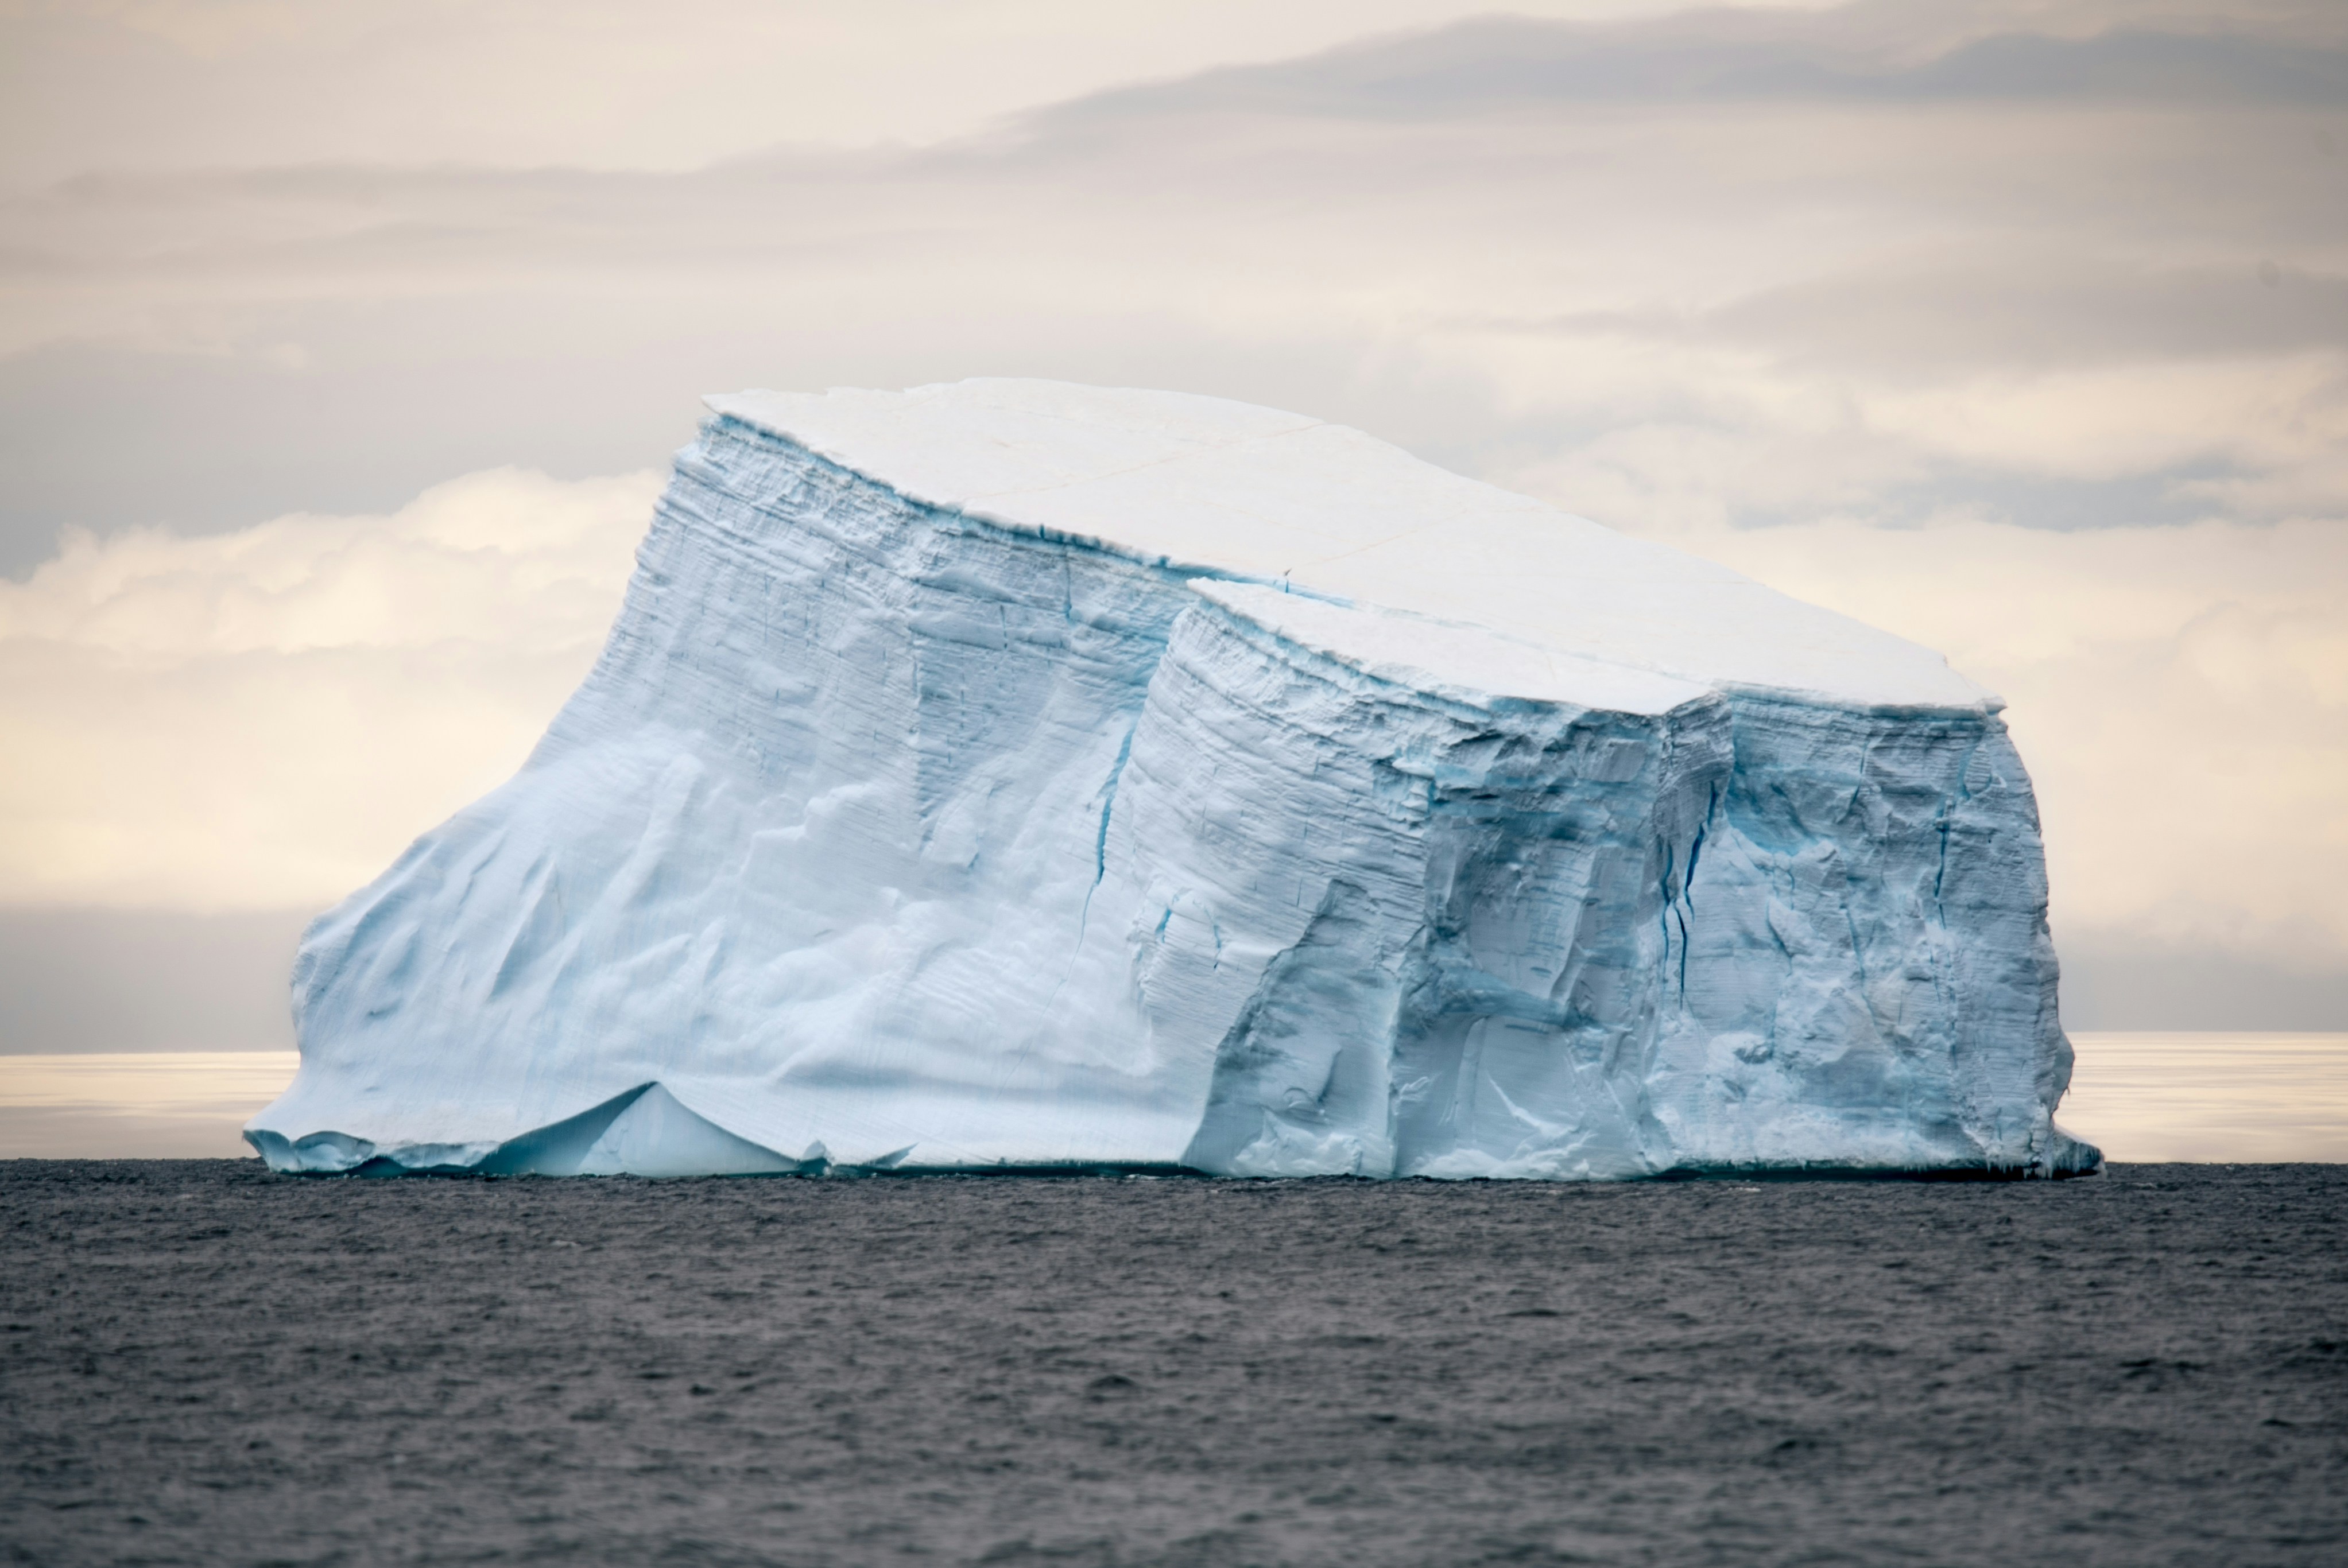
How do we reduce deaths in traffic?
How do we reduce deaths in traffic?
- Traffic laws
- Road Design
- Assistance systems
- Brakes
- Seatbelts
- Airbags
- Crumple zones
- Ambulances
Defense in Depth!
Defense in Depth!
- Security policies and standards
- Secure-by-design architecture
- System hardening
- Patching and vulnerability management
- Phishing-resistant authentication
- Least privilege
- Network segmentation
- Intrusion detection and monitoring
- Incident response
- Backups and disaster recovery
Common Sense
Because common sense often... isn't.
The User is the Weakest Link.
The User is the Weakest Link.
- They reuse passwords
- They click away warnings
- They send email to the wrong people
- They open any attachments
Yes, humans make mistakes.
We knew that when we designed the systems.
A resilient system assumes human error.
One mistake -> Catastrophe!
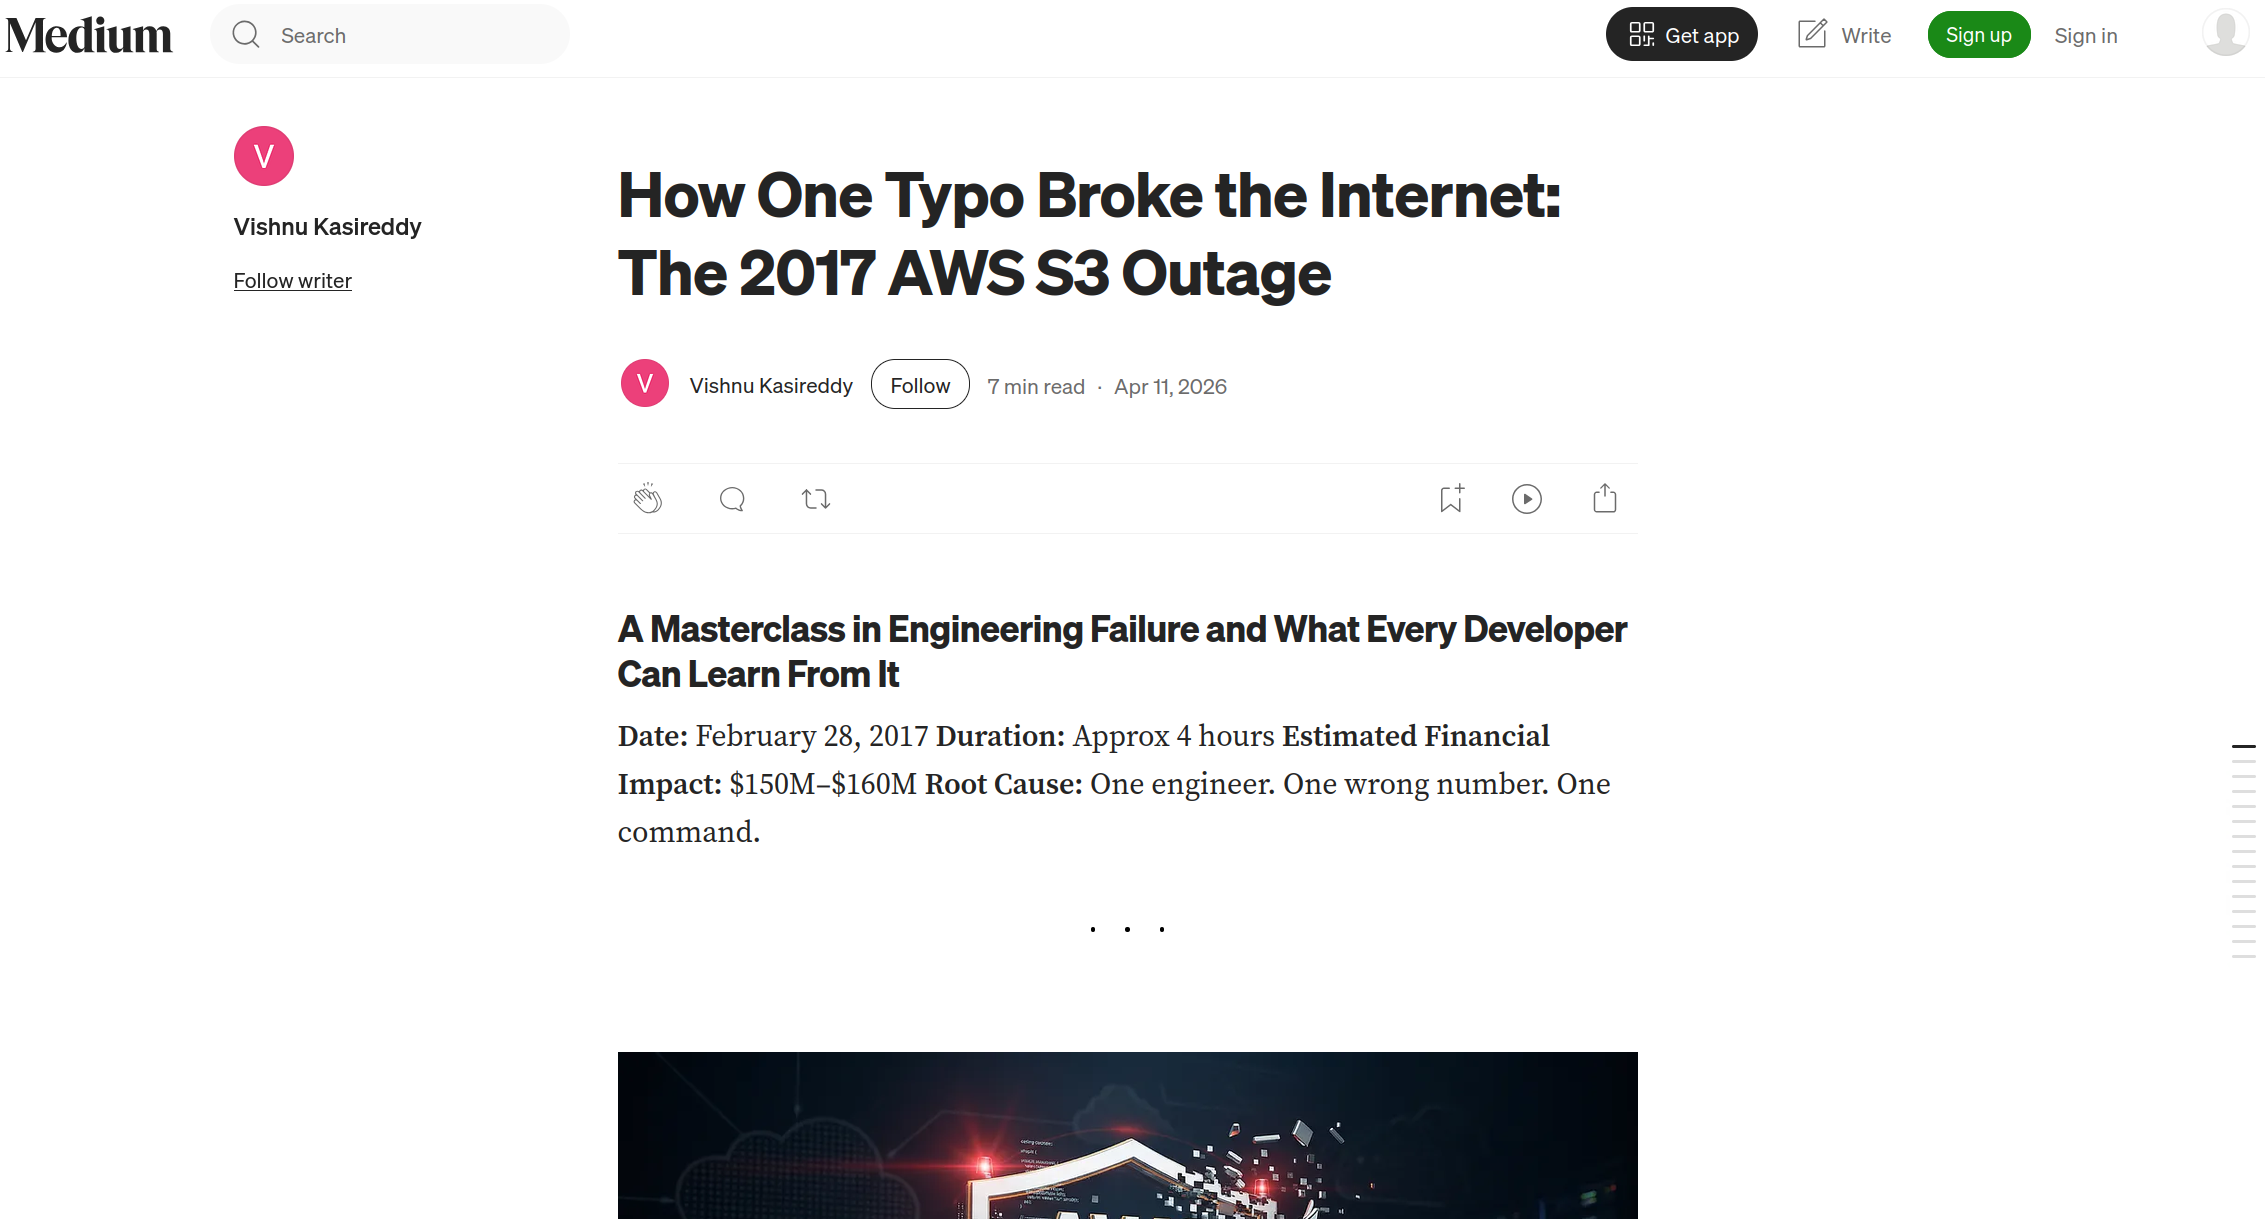
If a single typo can
bring down your infrastructure,
the problem isn't the typo.
- Least Privilege
- Dual control (4-Eyes Principle)
- Operational Safeguards
- Capacity Limits
- Safe defaults
- Containment/segmentation
- Tested Recovery Procedures
The User is not a Security Control!
If your systems depend on an infallible user
they are not resilient.
This System is only Reachable
from the Inside
It requires less security attention
The System was Only Reachable from the Inside.
The Fish Tank wasn't.
If you don't have a Fish Tank:
If you don't have a Fish Tank:
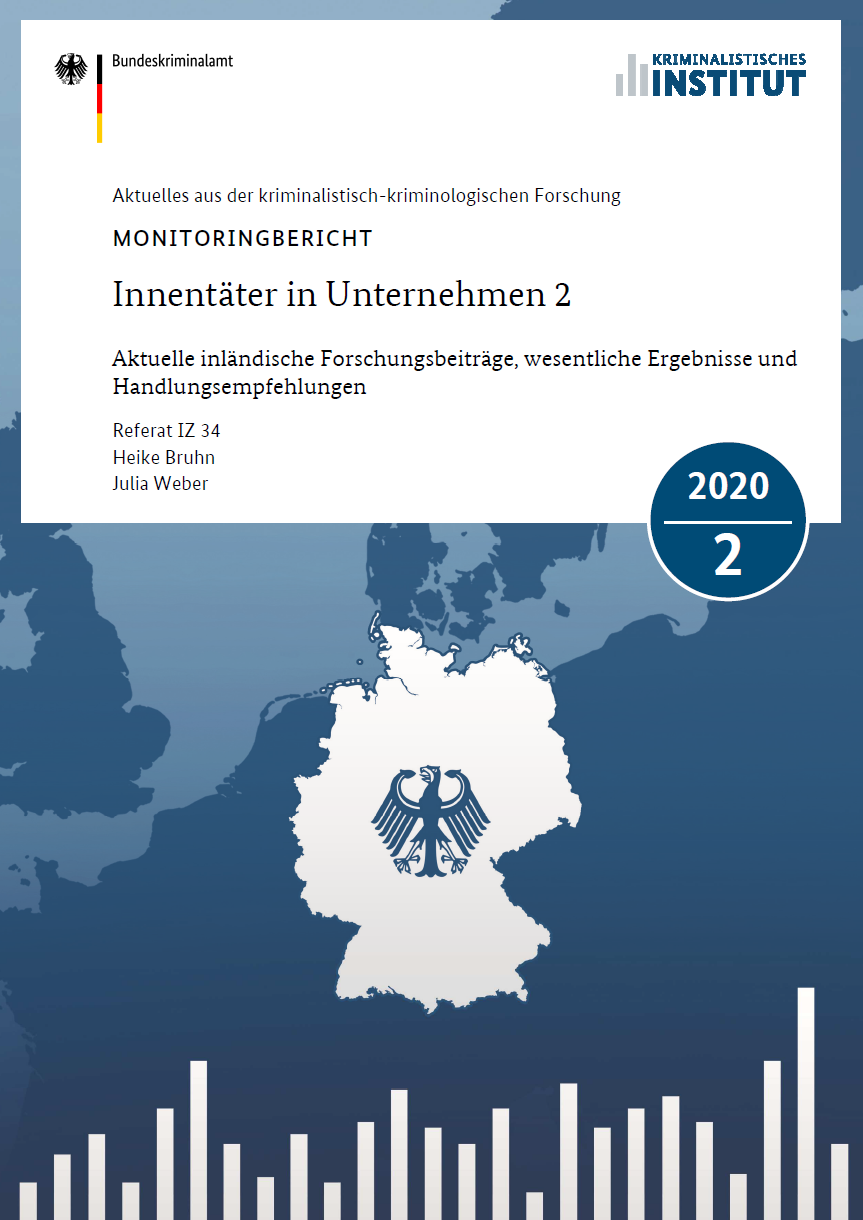
Two thirds of the companies affected (68%) stated that they had been harmed in particular by former employees or their own current employees.
"By a considerable margin, the largest group of perpetrators remains within the organisation itself."
In most cases, the opportunity to commit the offence is created while the person is still actively employed.
(Bundeskriminalamt, Germany)
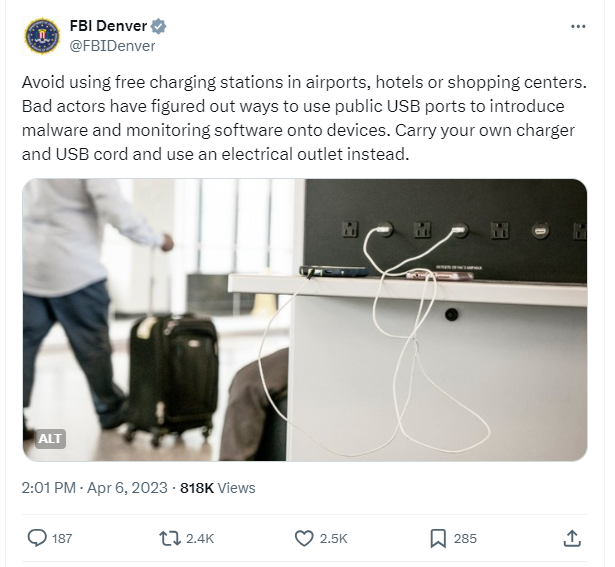
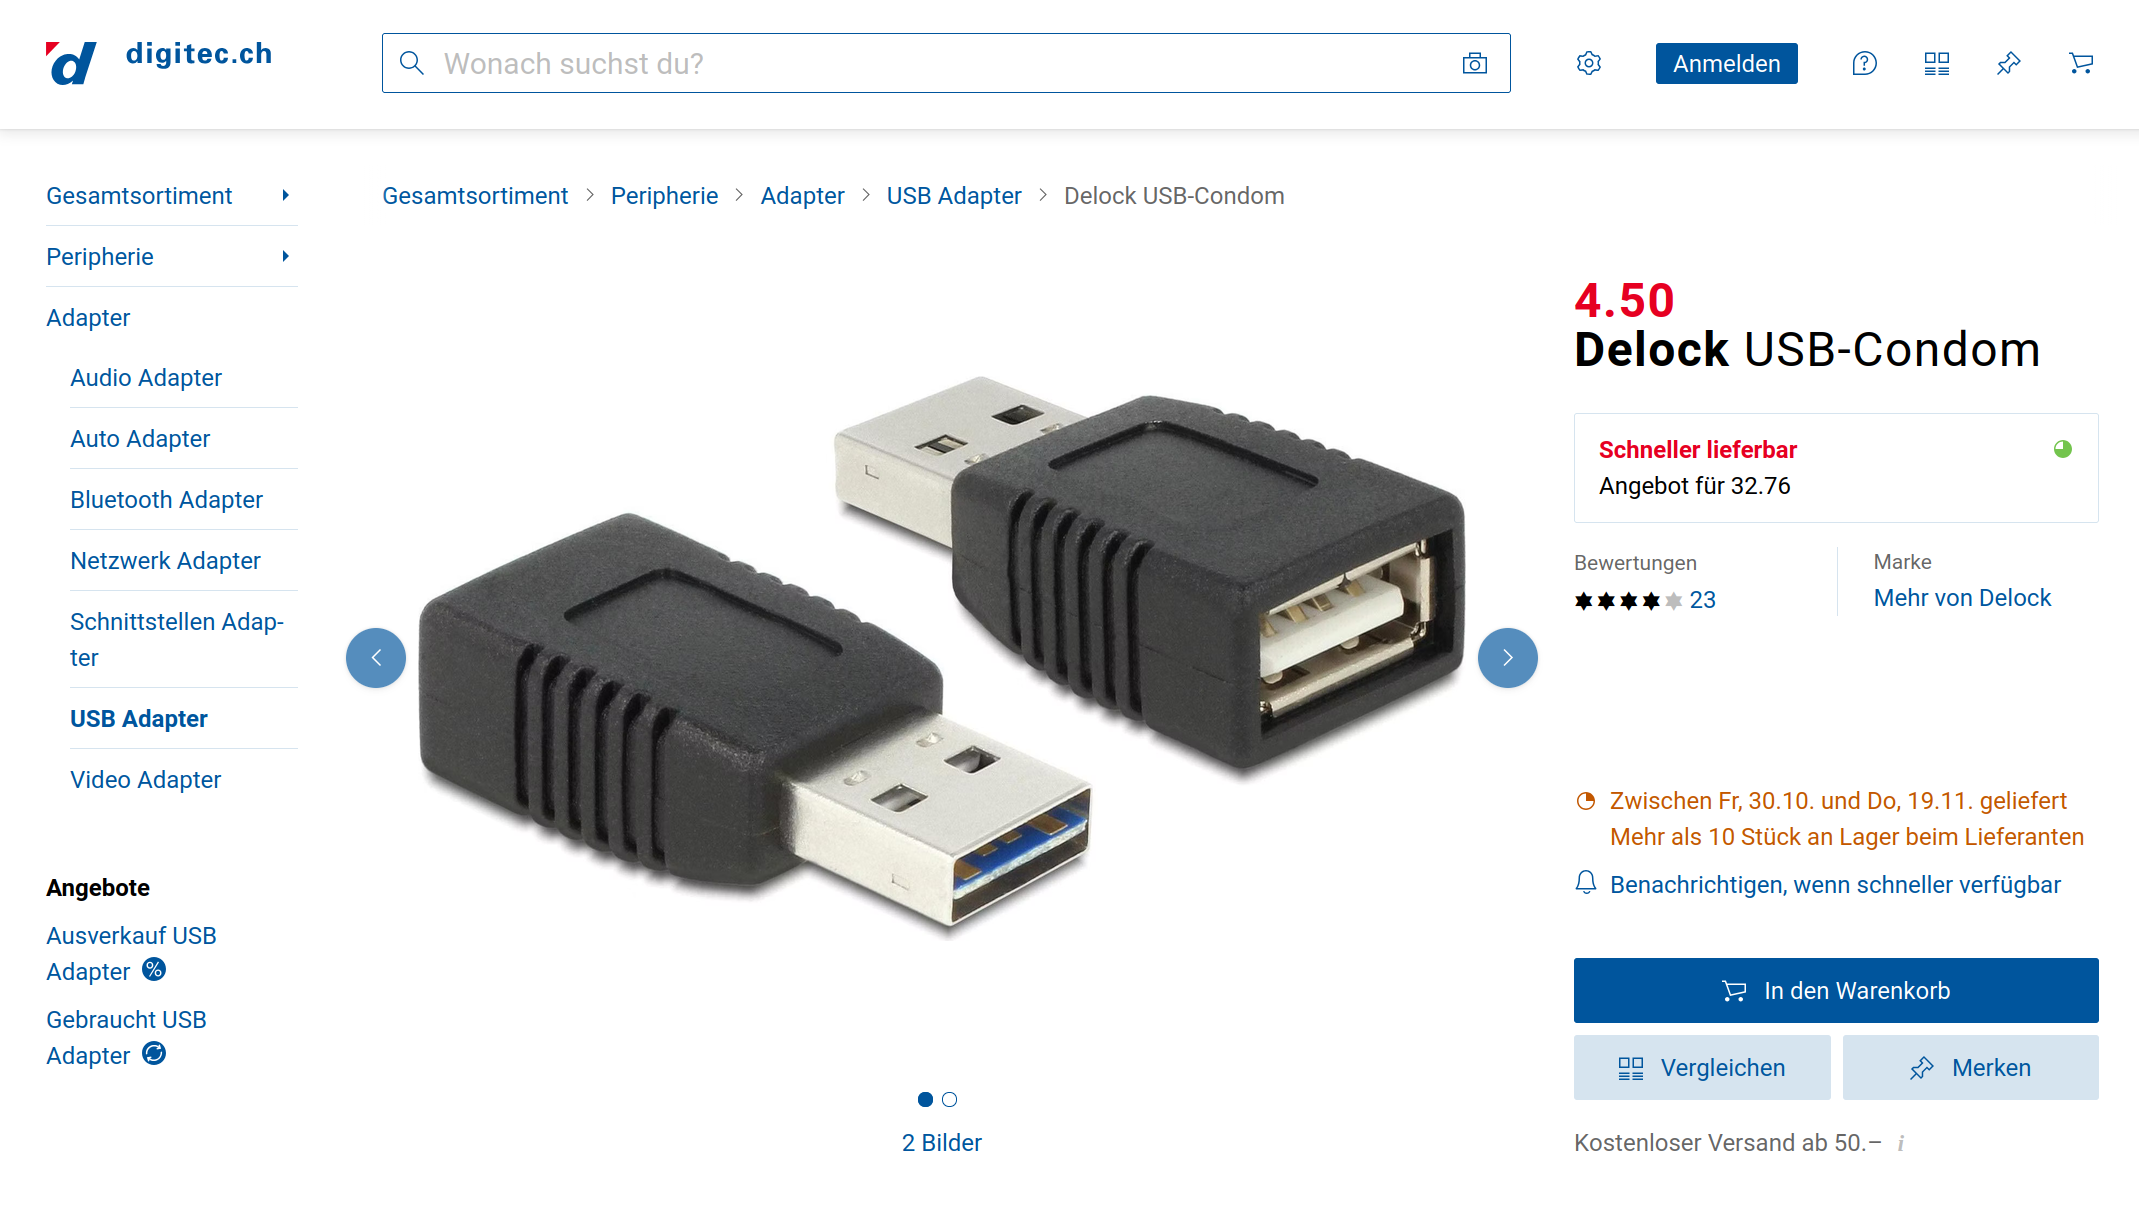
Juice Jacking
Never use public USB ports!
As seen at:
As seen at:
FBI
As seen at:
Fortune
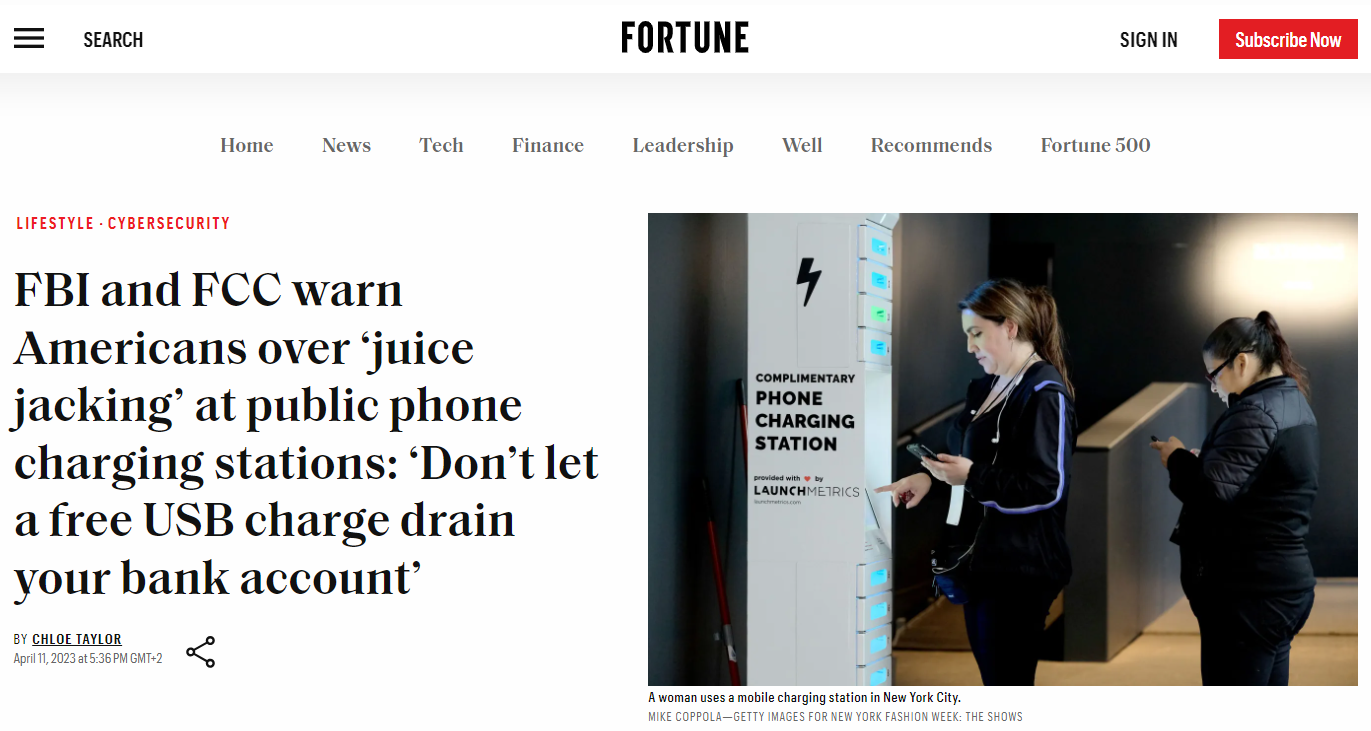
As seen at:
Washington Post
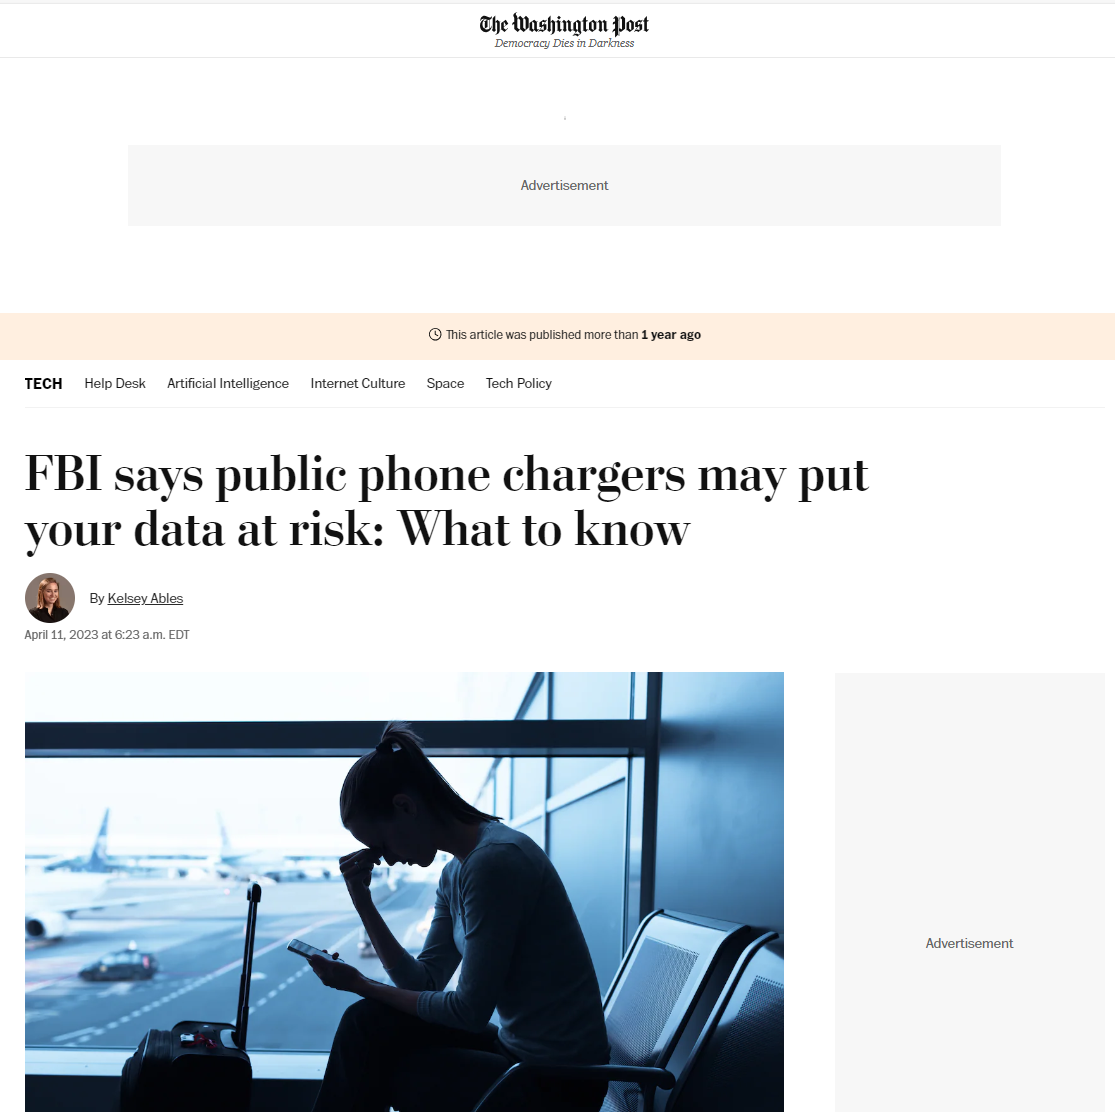
As seen at:
BIT
The Truth:
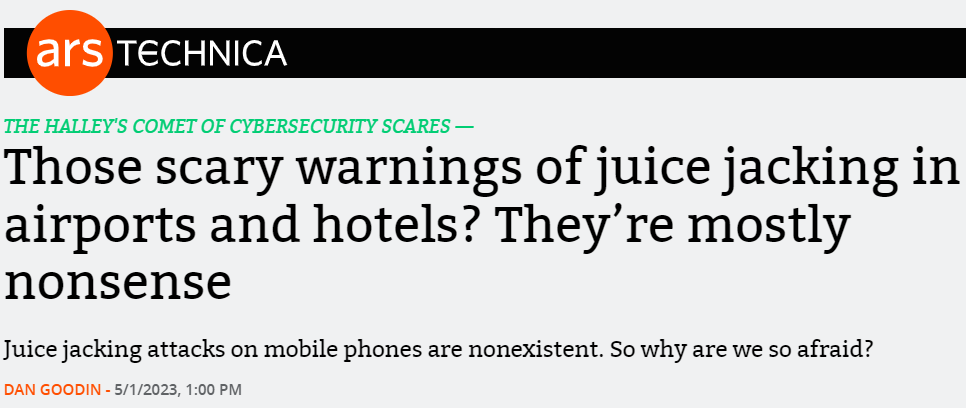
The Truth:
Demonstrated once (at DefCon)
Subsequently demonstrated by other researchers.
Picked up by the FBI
Repeated until ‘possible’ quietly became ‘common’.
The Truth:
Actual reported cases:
0
The Truth:
There are no questions!
Photo Attributions
| Photo | Source |
|---|---|
| Odyssey | British Museum |
| Entropy table | /u/HelmedHorror |
| Shisa kanko: | デスタサトリア |
| Peter Gutmann: | Wikipedia (Peter Gutmann) |
| Titanic: | Public Domain |
| Iceberg: | Hubert Neufeld |
| Casino: | Kaysha |
| Aquarium: | Elist Nguyen |

All others: Adrian A. Baumann (occasionally with AI assistance)